
Ransomware & Malware BleepingComputer 3 weeks ago

ShinyHunters hacks Clop leak site, threatens to extort ransomware gang

CN
CyberNew Threat Research Desk
• Original Reporting: BleepingComputer
CyberNew Threat Intel Assessment
Assessed Severity: CRITICAL
Impacted Surface
Enterprise Data & Identity Stores
Intelligence Sector
Ransomware & Malware

Analyst Takeaway

"The ShinyHunters extortion gang breached the Clop (aka Cl0p) ransomware operation's data leak site, defacing the Tor site and allegedly stealing server data and the private keys for its onion service. The attack began Friday night when ShinyHunters exploited what they claim is an unauthenticated file upload vulnerability in Grav CMS, which they used to upload a small text file to Clop's site...."

Recommended Defense & Mitigation

  • Emergency Patching: Prioritize vendor patches and CVE mitigation across internet-facing assets immediately.
  • Perimeter Audit: Inspect perimeter firewall logs and hunt for unauthorized RCE indicators.
Curated & Verified by CyberNew Threat Intelligence Desk Standard Defense Framework (NIST / MITRE ATT&CK)

Smiling hacker

The ShinyHunters extortion gang breached the Clop (aka Cl0p) ransomware operation's data leak site, defacing the Tor site and allegedly stealing server data and the private keys for its onion service.

The attack began Friday night when ShinyHunters exploited what they claim is an unauthenticated file upload vulnerability in Grav CMS, which they used to upload a small text file to Clop's site.
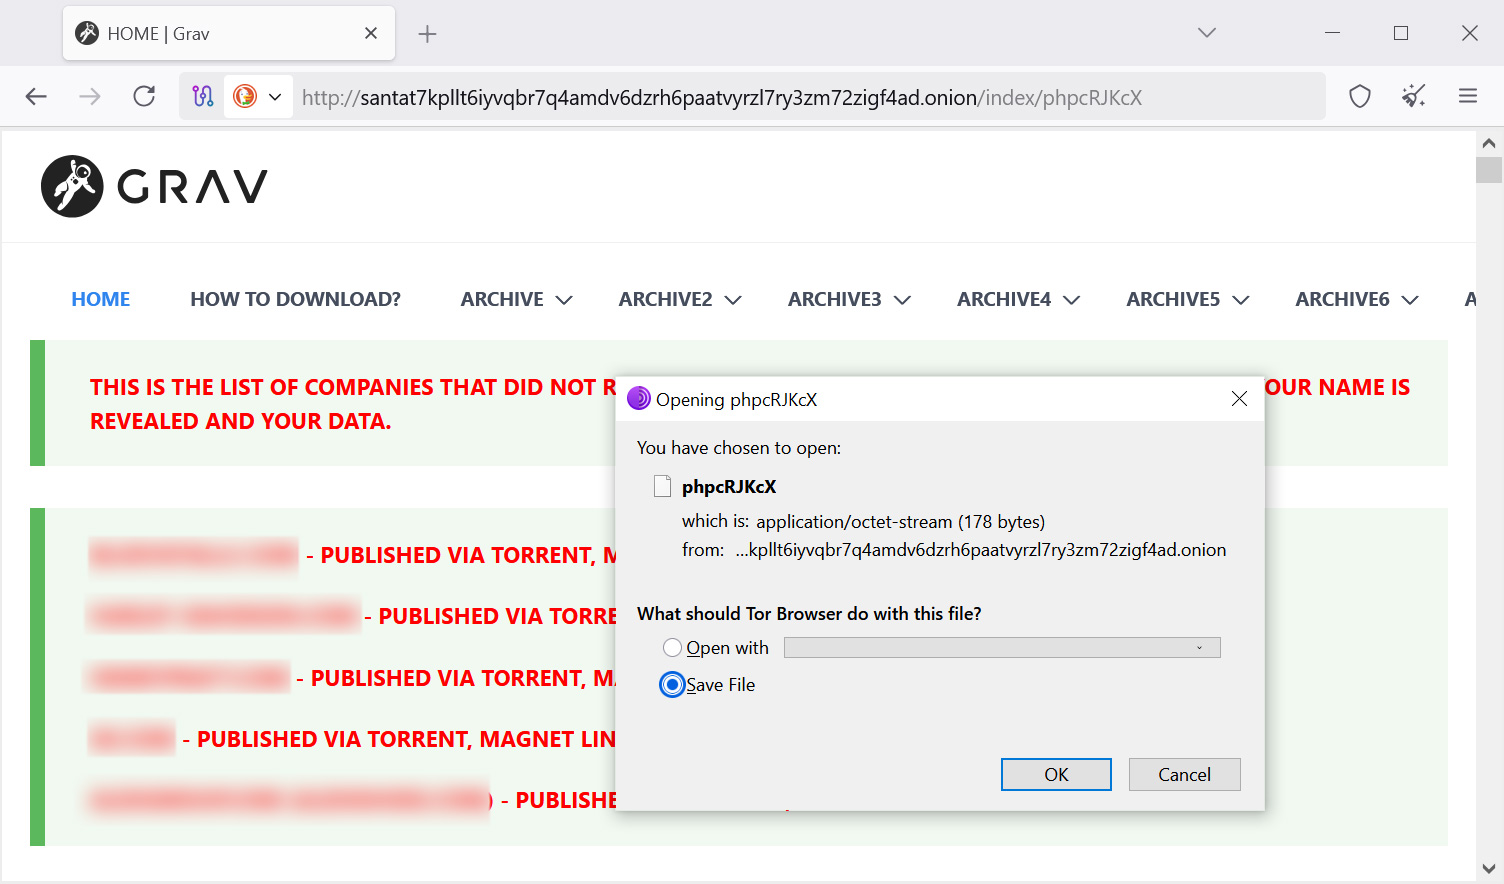
File downloaded from Clop's data leak site
Source: BleepingComputer

The small text file contained a message from the threat actors to the Clop ransomware gang, warning not to threaten them and including a link to ShinyHunter's own data leak site.

"THIS SITE HAS BEEN PWN3D BY SHINYHUNTERES #Skids10p - Maybe don't try to threaten us next time," read the uploaded file.
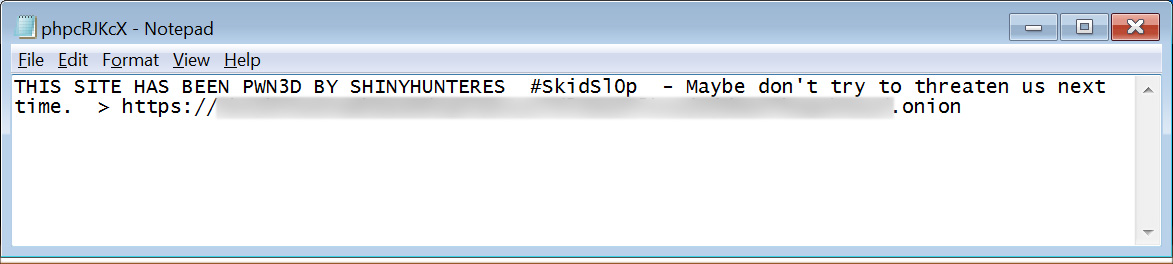
File uploaded to Clop's data leak site
Source: BleepingComputer
Save your seat

Source Verification & Original Intelligence

This threat report was reviewed by CyberNew analysts and cross-referenced with primary security disclosures from BleepingComputer.

Primary Advisory →