

The summer of 2026 taught the security industry a new phrase: the stolen AI login. In late August, as BleepingComputer reported, Anthropic responded to infostealer-driven hijacking of Claude sessions by signing users out, wiping saved payment methods, and refunding charges it identified as unauthorized.
That is the supply side. SOCRadar's AI Identity Exposure Report goes after the demand side: the enterprises whose employees are the credentials being sold.
Starting from more than one million infostealer records tied to AI services across 80,000-plus corporate domains, the research narrowed the set to 482 major established enterprises to answer a single question: when an AI login lands in a stealer log, whose is it, and what does the buyer inherit?
Of the 482, 68% are billion-dollar organizations across 36 countries and eight sectors, concentrated in North America, dozens of them Forbes-ranked.
Between them sit 5,434 stealer-log records tied to 1,500 distinct corporate email addresses, and 295 of the 482 surfaced in the last 90 days.
ChatGPT dominates the dataset; Hugging Face and Replit show developer tools are exposed as well
Break the dataset down by platform and one name swallows the chart. A captured ChatGPT or OpenAI session shows up for 358 of the 482 companies, and those companies carry roughly 90% of all records in the study. Zapier, Notion, Hugging Face, Replit, Lovable, and ElevenLabs trail far behind.
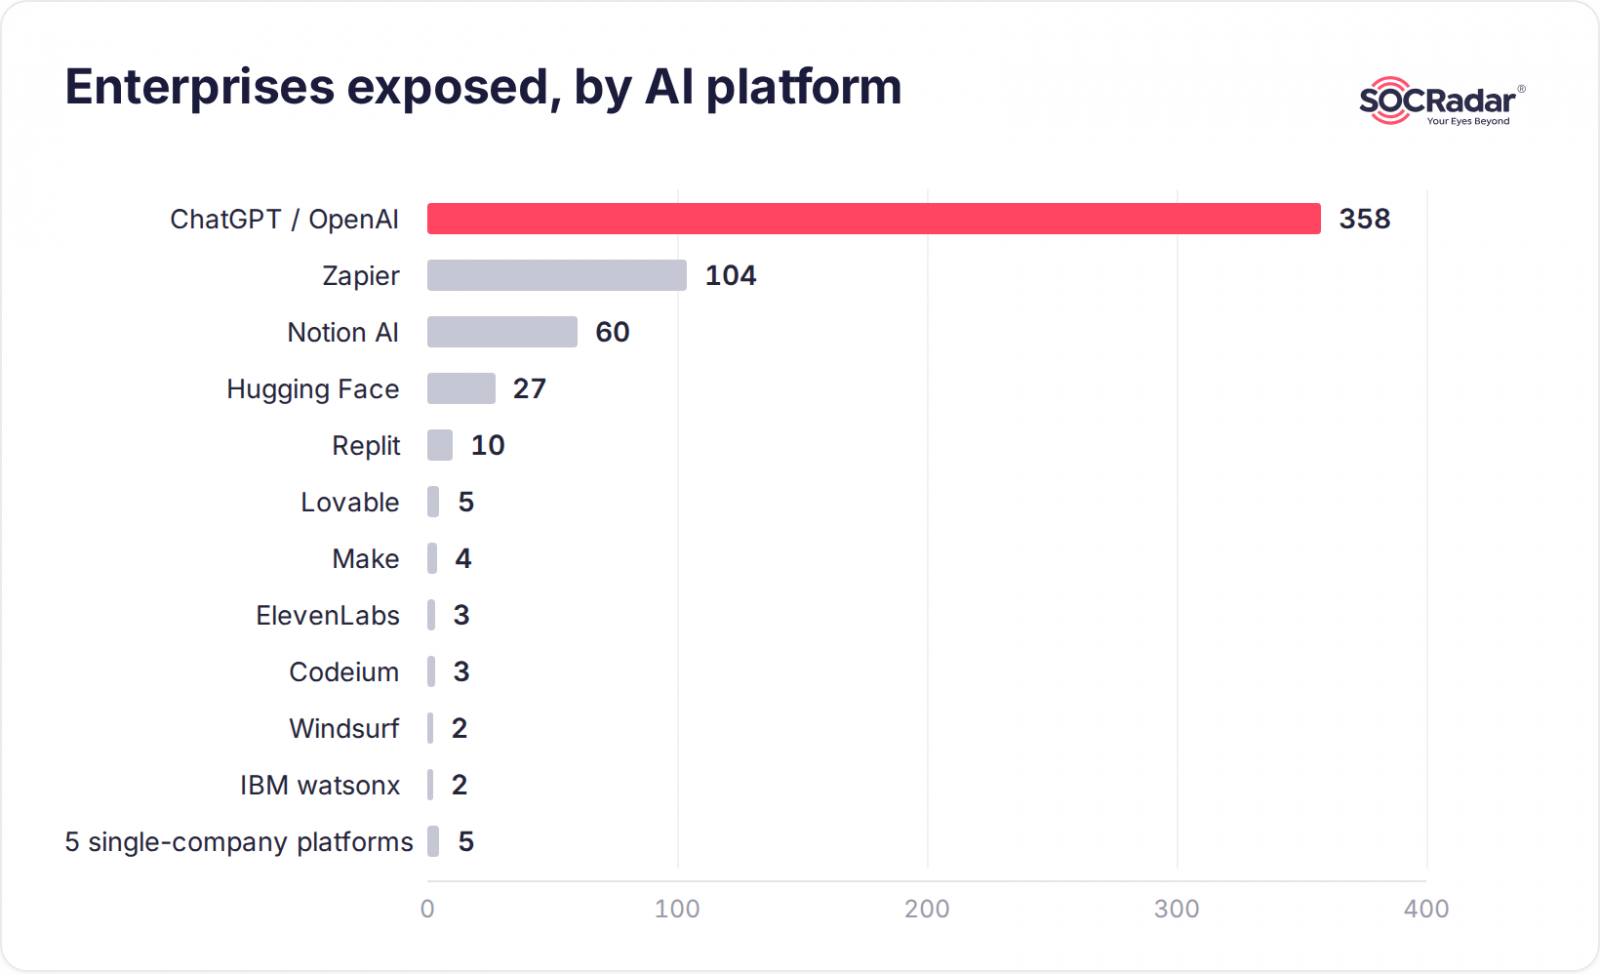
That skew matters, but the more interesting part is who is missing. There is no Claude in the top ranks. No Gemini.