
Threat Intelligence & APT The Record 1 month ago

Berlin investigates new data leak after hackers publish stolen login credentials

CN
CyberNew Threat Research Desk
• Original Reporting: The Record
CyberNew Threat Intel Assessment
Assessed Severity: INFORMATIONAL
Impacted Surface
Enterprise Data & Identity Stores
Intelligence Sector
Threat Intelligence & APT

Analyst Takeaway

"Berlin. Image: Ro Berto via Pexels Berlin investigates new data leak after hackers publish stolen login credentials German authorities are investigating another trove of data stolen from Berlin’s government network after hackers published login credentials and other information over the weekend. The latest release follows a cyberattack discovered in mid-August that compromised two Berlin..."

Recommended Defense & Mitigation

  • Threat Monitoring: Ingest published IOCs into SIEM/EDR detection rules for continuous telemetry monitoring.
  • Security Awareness: Alert staff and maintain baseline endpoint hardening across endpoints.
Curated & Verified by CyberNew Threat Intelligence Desk Standard Defense Framework (NIST / MITRE ATT&CK)
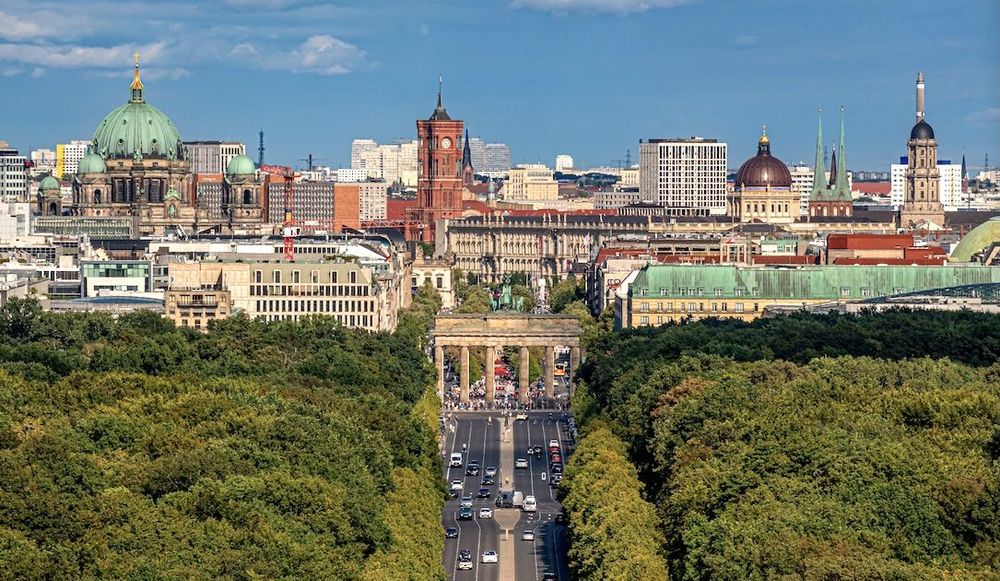
Berlin
Berlin. Image: Ro Berto via Pexels

Berlin investigates new data leak after hackers publish stolen login credentials

German authorities are investigating another trove of data stolen from Berlin’s government network after hackers published login credentials and other information over the weekend.

The latest release follows a cyberattack discovered in mid-August that compromised two Berlin ministries responsible for urban development and housing, and for transport, mobility, climate protection and the environment.

Berlin’s government said Sunday that the newly released data includes login credentials but did not say what systems they could be used to access or whether they were still valid. The authorities have not attributed the attack to a specific threat actor.

The city’s urban development ministry has strengthened security measures introduced after an earlier data leak, which officials said could temporarily limit access to some of its applications.

Source Verification & Original Intelligence

This threat report was reviewed by CyberNew analysts and cross-referenced with primary security disclosures from The Record.

Primary Advisory →