
Threat Intelligence & APT The Record 3 weeks ago

EU data regulator fines Google more than $460 million for location data violations

CN
CyberNew Threat Research Desk
• Original Reporting: The Record
CyberNew Threat Intel Assessment
Assessed Severity: INFORMATIONAL
Impacted Surface
Enterprise Perimeter & Network Defense
Intelligence Sector
Threat Intelligence & APT

Analyst Takeaway

"Google's European headquarters are located in Dublin, Ireland. Credit: Stephen Bergin / Unsplash EU data regulator fines Google more than $460 million for location data violations Ireland’s Data Protection Commission (DPC) will fine Google more than €403 million ($462 million) for the tech giant’s processing of location data, the regulator said Monday, concluding an inquiry into the company that..."

Recommended Defense & Mitigation

  • Threat Monitoring: Ingest published IOCs into SIEM/EDR detection rules for continuous telemetry monitoring.
  • Security Awareness: Alert staff and maintain baseline endpoint hardening across endpoints.
Curated & Verified by CyberNew Threat Intelligence Desk Standard Defense Framework (NIST / MITRE ATT&CK)
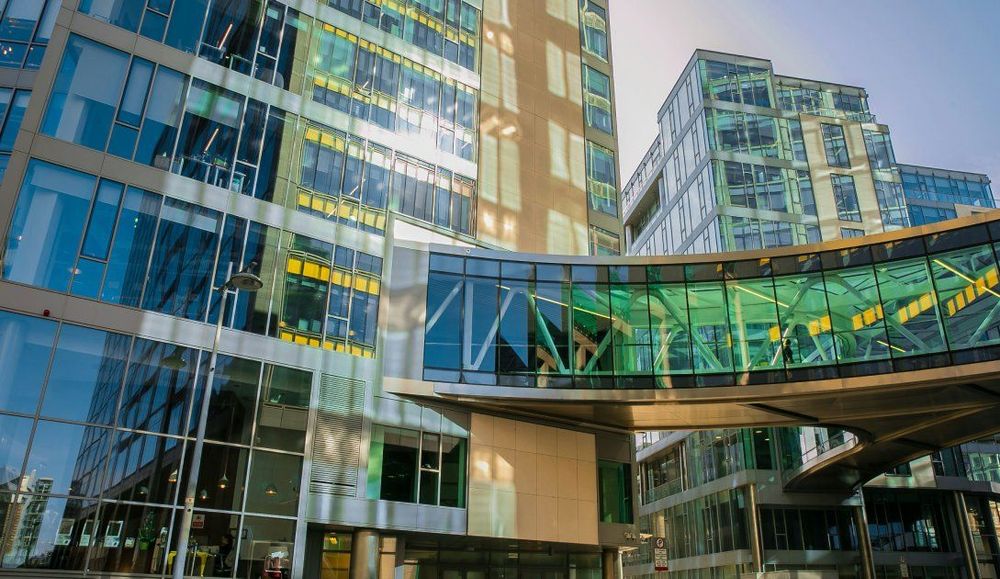
Google Dublin
Google's European headquarters are located in Dublin, Ireland. Credit: Stephen Bergin / Unsplash

EU data regulator fines Google more than $460 million for location data violations

Ireland’s Data Protection Commission (DPC) will fine Google more than €403 million ($462 million) for the tech giant’s processing of location data, the regulator said Monday, concluding an inquiry into the company that began in February 2020.

Google has also been ordered to fix its data processing practices within six months, according to the regulator’s press release. The DPC is the European Union’s lead supervisory authority charged with overseeing Google’s data protection practices because the platform’s European headquarters are based in Dublin. 

The inquiry began more than six years ago after several European consumer rights groups asked the DPC to look into Google’s practices, which allegedly violated Europe’s General Data Protection Regulation (GDPR). 

The inquiry focused on how Google processes location data in connection with three of its services and features: web and app activity, location history and location accuracy, the DPC said. Google’s practices allegedly violated GDPR due to how it tracked and stored the location data.

The inquiry examined Google’s data processing norms beginning in May 2018 — when GDPR became law — through February 2020.

Source Verification & Original Intelligence

This threat report was reviewed by CyberNew analysts and cross-referenced with primary security disclosures from The Record.

Primary Advisory →