
Cyber News BleepingComputer 2 days ago

Global takedown hits network behind 1 billion phishing messages

CN
CyberNew Threat Research Desk
• Original Reporting: BleepingComputer
CyberNew Threat Intel Assessment
Assessed Severity: CRITICAL
Impacted Surface
Enterprise Perimeter & Network Defense
Intelligence Sector
Cyber News

Analyst Takeaway

"A massive cybercriminal ecosystem facilitating more than a billion malicious messages targeting over 75,000 organizations across 150 countries has been disrupted by law enforcement agencies and partners worldwide. Since the start of the year, more than 750 million malicious messages have been aimed at Microsoft customers via email and SMS texts. Following an investigation initiated by Microsoft..."

Recommended Defense & Mitigation

  • Emergency Patching: Prioritize vendor patches and CVE mitigation across internet-facing assets immediately.
  • Perimeter Audit: Inspect perimeter firewall logs and hunt for unauthorized RCE indicators.
Curated & Verified by CyberNew Threat Intelligence Desk Standard Defense Framework (NIST / MITRE ATT&CK)

Global takedown hits network behind 1 billion phishing messages

A massive cybercriminal ecosystem facilitating more than a billion malicious messages targeting over 75,000 organizations across 150 countries has been disrupted by law enforcement agencies and partners worldwide.

Since the start of the year, more than 750 million malicious messages have been aimed at Microsoft customers via email and SMS texts.

Following an investigation initiated by Microsoft and Japan’s National Police Agency (NPA) into a wave of fraudulent activity, "a sprawling Chinese-language cybercrime marketplace" was discovered, with tools and services for phishing campaigns.

The investigators traced the malicious activity to YAM Store (Storm-3119), an underground infrastructure marketplace, then linked it to the CoGUI, Haozi, and Iron Man System phishing kits, collectively tracked as Storm-2990.
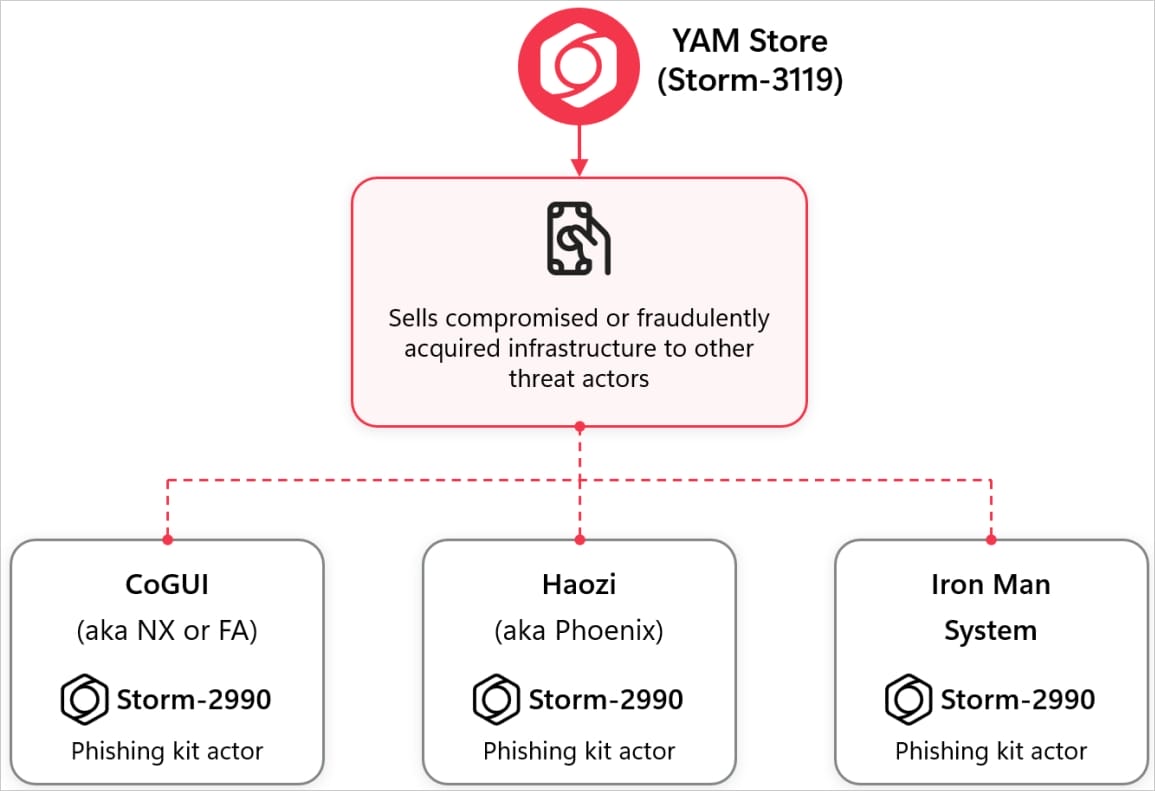
Operational overview
Source: Microsoft
Save your seat

Source Verification & Original Intelligence

This threat report was reviewed by CyberNew analysts and cross-referenced with primary security disclosures from BleepingComputer.

Primary Advisory →