
Cyber News Isc 2 days ago

Orphaned VBA Projects Inside DWG Files, (Wed, Oct 14th)

CN
CyberNew Threat Research Desk
• Original Reporting: Isc
CyberNew Threat Intel Assessment
Assessed Severity: CRITICAL
Impacted Surface
Enterprise Perimeter & Network Defense
Intelligence Sector
Cyber News

Analyst Takeaway

"Years ago I wrote diary entries about VBA code stored inside AutoCAD drawing files (.dwg). In a nutshell: the VBA code is stored inside an OLE file, that is embedded inside the DWG file. You can do a brute-force search for the embedded OLE file, or you can follow a pointer inside the header of the DWG file. I wrote a small Python script ( autocad.py ) for this second case. It looks at a 32-bit..."

Recommended Defense & Mitigation

  • Emergency Patching: Prioritize vendor patches and CVE mitigation across internet-facing assets immediately.
  • Perimeter Audit: Inspect perimeter firewall logs and hunt for unauthorized RCE indicators.
Curated & Verified by CyberNew Threat Intelligence Desk Standard Defense Framework (NIST / MITRE ATT&CK)

Years ago I wrote diary entries about VBA code stored inside AutoCAD drawing files (.dwg).

In a nutshell: the VBA code is stored inside an OLE file, that is embedded inside the DWG file. You can do a brute-force search for the embedded OLE file, or you can follow a pointer inside the header of the DWG file.

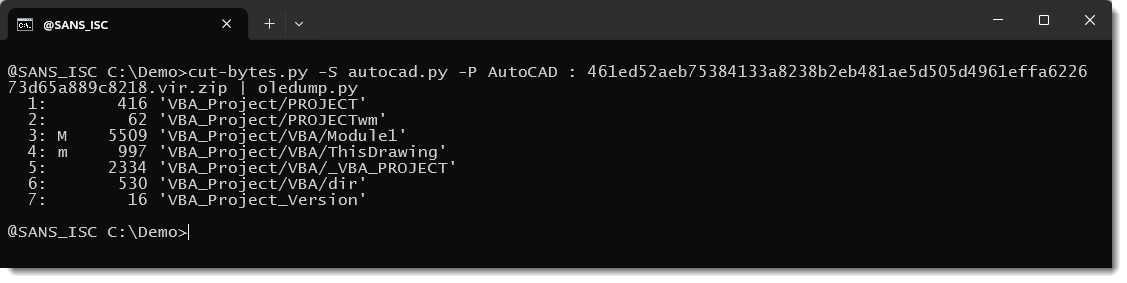
I wrote a small Python script (autocad.py) for this second case. It looks at a 32-bit pointer at position 0x24 inside the DWG file. This points to a 16-byte long header, followed by the embedded file. This 16-byte long header contains the length of the embedded file. You use the script together with my tool cut-bytes.py, like this:

cut-bytes.py -S autocad.py -P AutoCAD : 461ed52aeb75384133a8238b2eb481ae5d505d4961effa622673d65a889c8218.vir.zip | oledump.py
Source Verification & Original Intelligence

This threat report was reviewed by CyberNew analysts and cross-referenced with primary security disclosures from Isc.

Primary Advisory →