

[This is a Guest Diary by Zachary Norwood, an ISC intern as part of the SANS.edu BACS program]
Crypto mining malware has been active and spreading across the internet for quite some time now. Moreover, the DShield honeypot picked up a worm that self-propagates through a plethora of means. One of them is stealing SSH keys after it gains access to a system. Furthermore, it also leverages a rootkit to maintain access to infected systems. One would hope that threat actors would have moved on past this worm by now. However, due to its rudimentary design and its effectiveness, they have had no reason to move on.
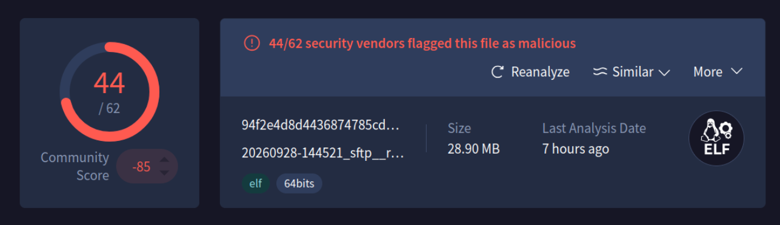
A malicious binary was uploaded and executed on the DShield honeypot, and that is where a copy of the Panchan worm was obtained. It is written with Golang, and it is a peer-to-peer botnet. Moreover, this worm was first identified in 2022. Many vendors recognize this worm now as seen below.
VirusTotal
Clamscan