

- CLOSEDQUORUM, a malware binary discovered through Cisco Talos’ CAIRN project, exhibits fully autonomous command and control (C2). While we do not have confirmation of in-the-wild deployment, artifacts from the binary were used to connect the developer to postings on criminal forums related to carding, dating back to 2025.
- This malware is a useful reference example of how attackers can collapse the decision space of a particular attack phase into a constrained set of choices, allowing AI models to provide reasoning and act independently.
- CLOSEDQUORUM represents a shift in effort displacement for attackers, in which expanding portions of the attack chain can be executed without operator involvement.
AI’s impact on offensive cyber operations has thus far mainly focused on two dimensions: speed and scale. Attackers can generate phishing lures faster and produce more malicious code variants with less effort. These are real effects, visible in the proliferation of AI-generated coding samples and agent-assisted intrusions that have become common in the past few years. But in each case, the human operator remains present: directing the tooling, selecting targets, and guiding the execution. AI makes the operator faster and more productive but does not remove them from the operation.
A third dimension has received less attention in the malware space: effort displacement. This is not merely augmenting what an operator can accomplish in a session but transferring an entire phase of the attack from the operator to the system. Effort displacement compounds the effects of speed and scale because the human-in-the-loop is no longer the bottleneck. Human operators are bound by attention, working hours, and cognitive load. An AI system capable of executing a phase of the attack chain can continue when the operator is no longer watching. It does not go offline when the attacker sleeps.
Today Cisco Talos released CAIRN, our open-source research toolkit for tracking AI-integrated malware. This is the first in a series of posts sharing what we've found. While the threat class of CAIRN findings may span from experimental proof-of-concept to sophisticated active campaigns, the nature of the threat is aside from the focus: actively studying this frontier provides actionable insights to offset how threat actors are operationalizing AI.
Introducing CLOSEDQUORUM
CLOSEDQUORUM is, to our knowledge, the first publicly documented Windows implant to apply this model to tactical command and control (C2). After deployment, it delegates the selection of its next action to a panel of commercial large language models (LLMs) and executes the resulting decision, with the intent of harvesting user credentials and crypto wallets. It does not require continued commands from a human operator or tasking from a dedicated, attacker-operated C2 server; the complete dynamic operation is delegated to the AI.
The name reflects the architecture. A quorum is a decision-making body that requires some minimum of participants to act. CLOSEDQUORUM's quorum is up to four LLM providers: DeepSeek, Qwen, Mistral, and Google Gemini. The session is closed; no humans are admitted. Four models are queried in sequence, their independent verdicts tallied, and the binary acts, based on their judgment.
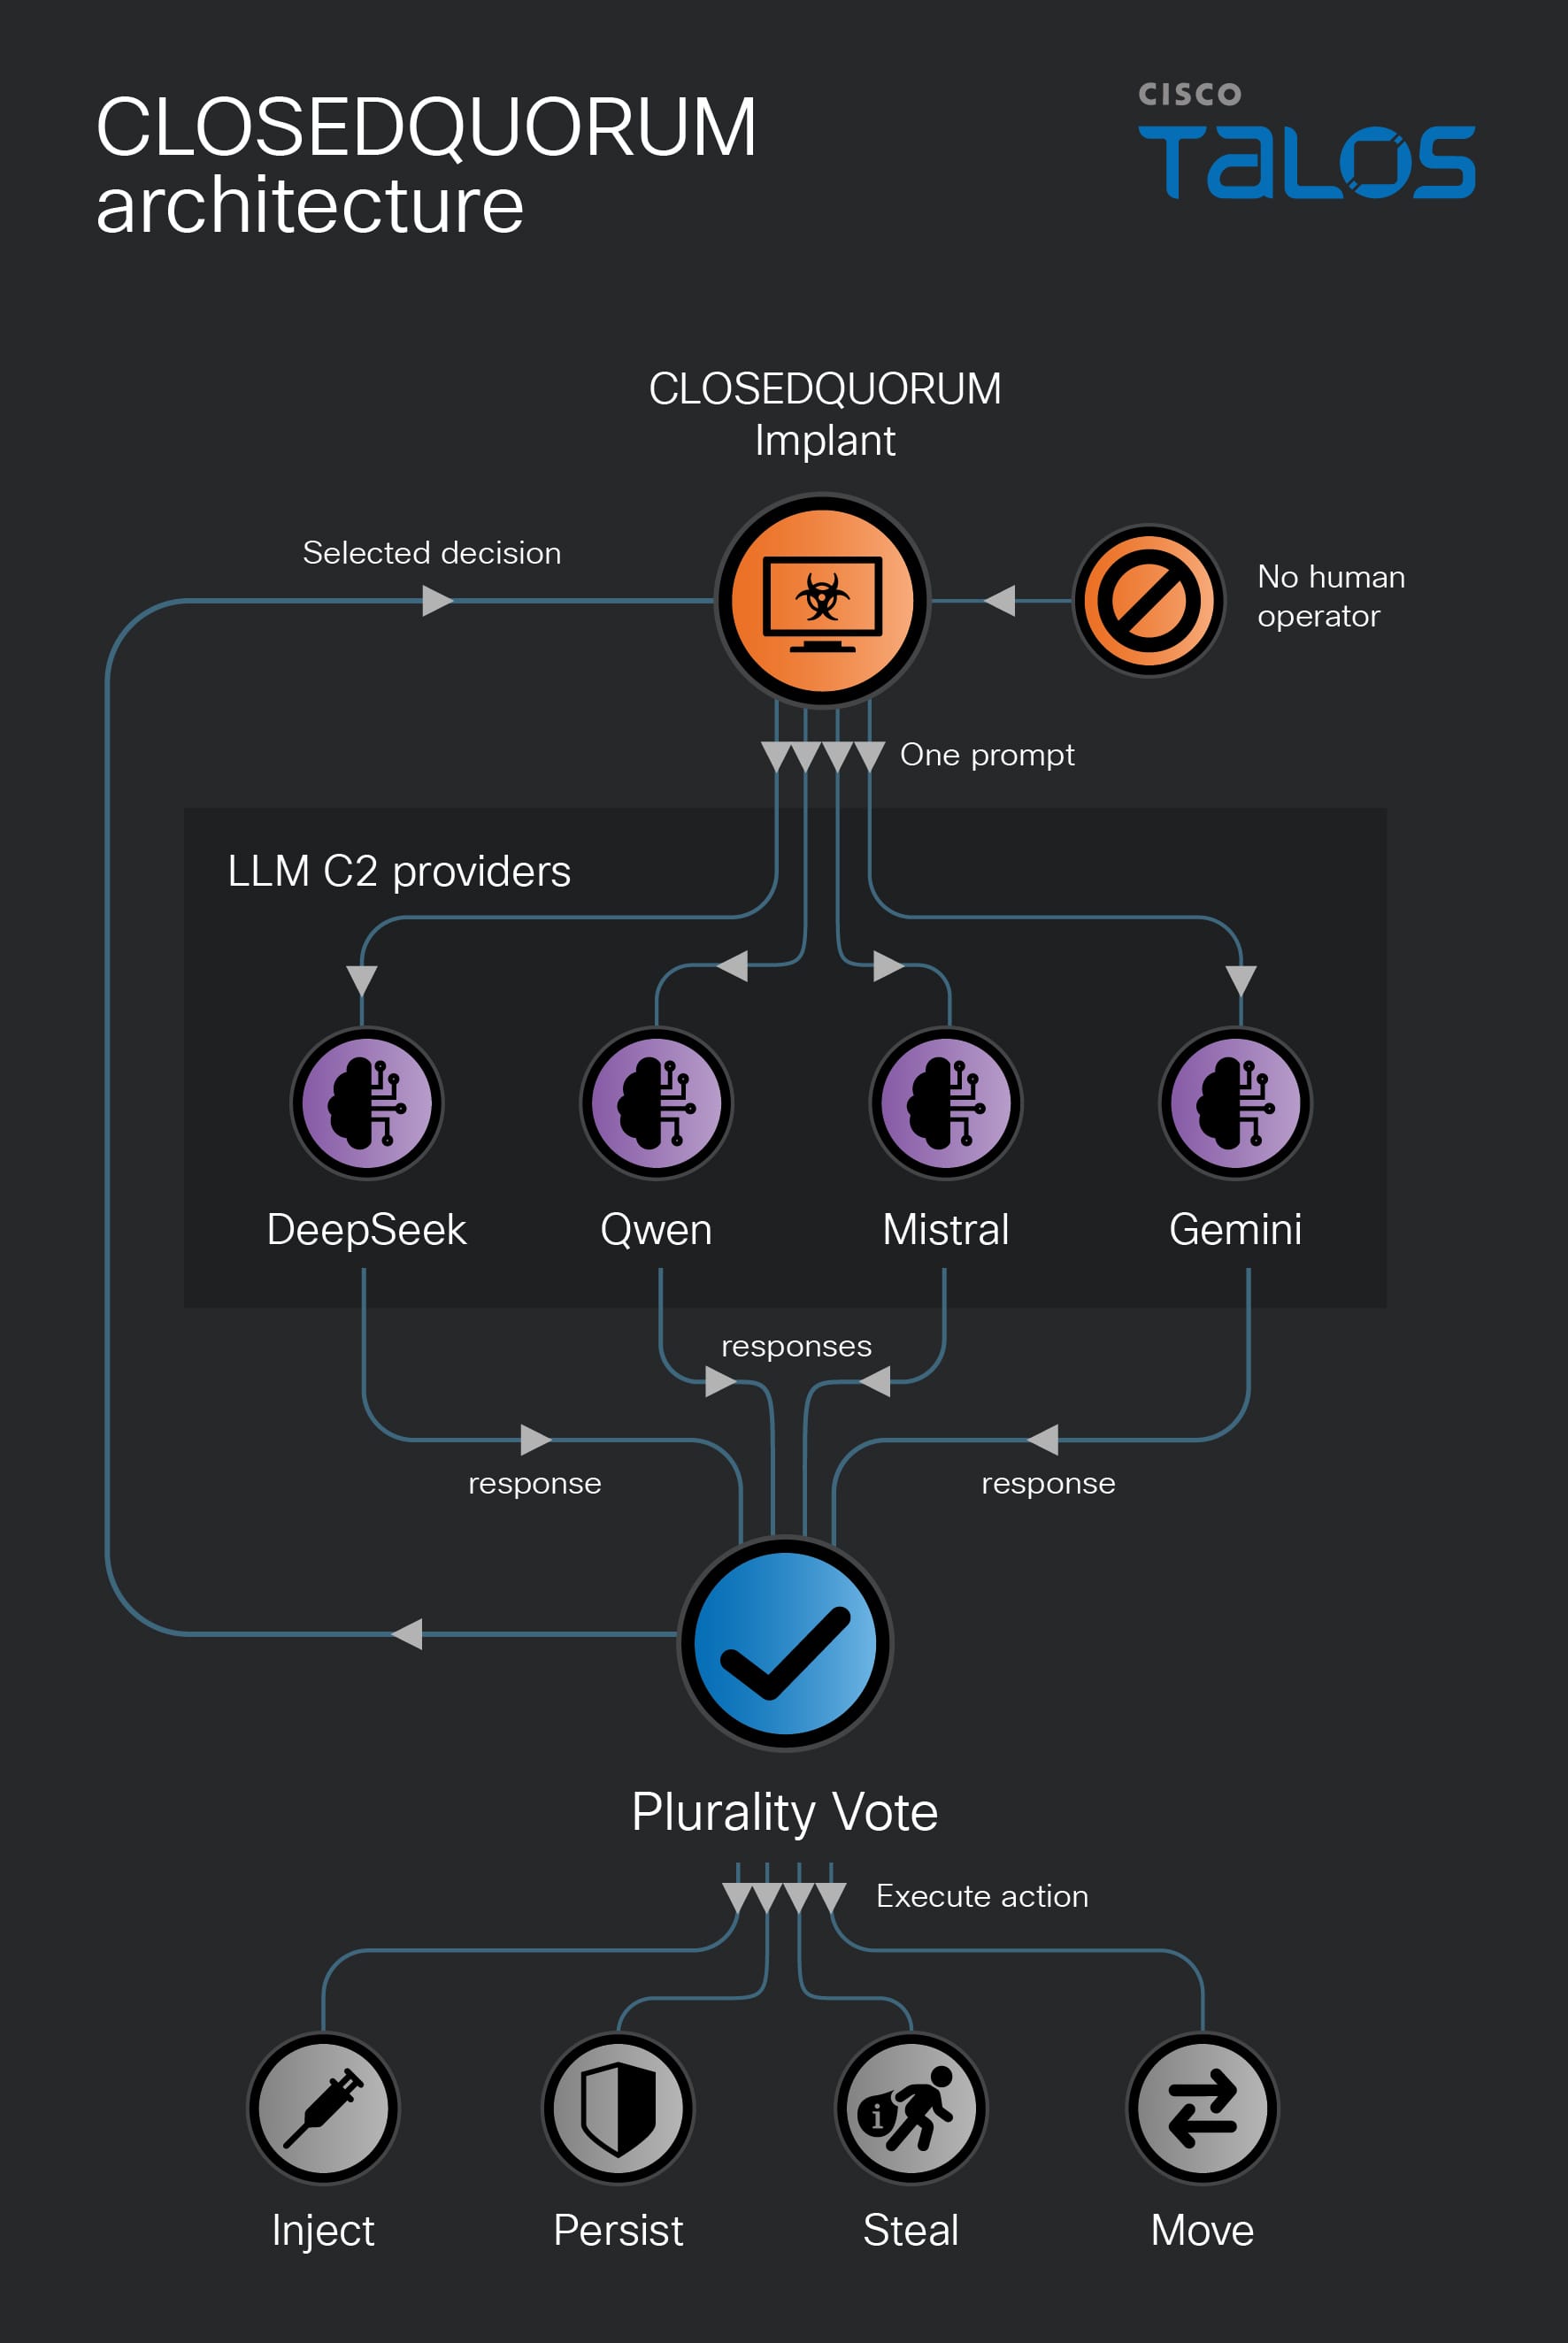
The CLOSEDQUORUM C2 architecture supports up to four LLM provider integrations. Each active model votes on the next action, and the action receiving the most votes is selected.
Our static analysis confirms the full details of the autonomous decision loop, and development builds demonstrate build-time injection of provider credentials. The public distribution build, however, contains placeholder API keys and a dummy webhook, so we did not observe a complete end-to-end execution of the architecture.
Further details of this post document how CLOSEDQUORUM works, what it can do, and what it means for the future of autonomous offensive AI tooling.
“LLM-as-C2" architecture
CLOSEDQUORUM is a 16.4MB, 64-bit Windows executable compiled in Go. It contains a range of offensive implant functionality, but that isn’t what makes it unique. The foundational design choice in CLOSEDQUORUM is the treatment of LLM providers as the C2 infrastructure.
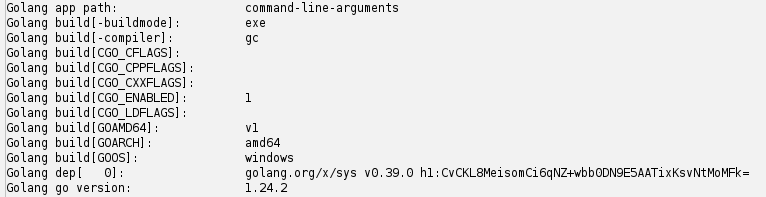
CGO_ENABLED=1 confirms the binary mixes Go and C code, which is how it makes direct Windows system calls. Traditional C2 architecture requires the attacker to operate server infrastructure: a domain, an IP, a protocol, and a listener. That infrastructure is attributable, blockable, and expensive to rotate. Defenders track C2 domains. Threat intelligence feeds publish C2 IPs. Certificate transparency logs expose new C2 infrastructure before it's used. Instead of a singular, unique C2 server, CLOSEDQUORUM calls up to four commercial LLM provider endpoints used by thousands of legitimate applications daily.
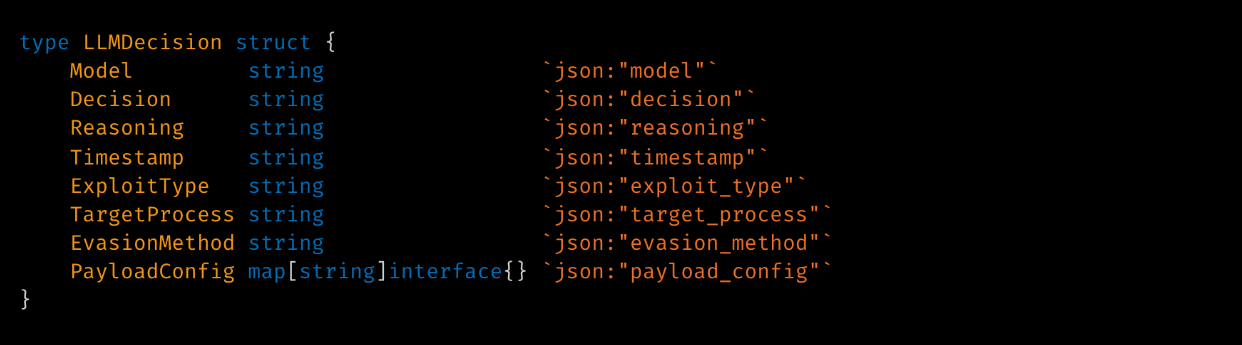
The providers are queried one-by-one by the ModelOrchestrator. Their responses are aggregated as a []LLMDecision slice and resolved by interModelDiscussion() into a single action via plurality voting: each provider's Decision field value increments a map[string]int counter, and the highest-count decision wins. The multi-provider design serves both aggregation and resilience, reducing the effect of individual refusals, timeouts, and malformed responses. It increases the likelihood of obtaining a valid decision but does not guarantee one.
Four providers increase the chance that the quorum reaches a decision even if one or two members are unresponsive, or for example, one model is hitting a guardrail. If all models fail, the fallback decision is consensus: a string with no corresponding capability handler, causing the loop to sleep and retry rather than take a default action.
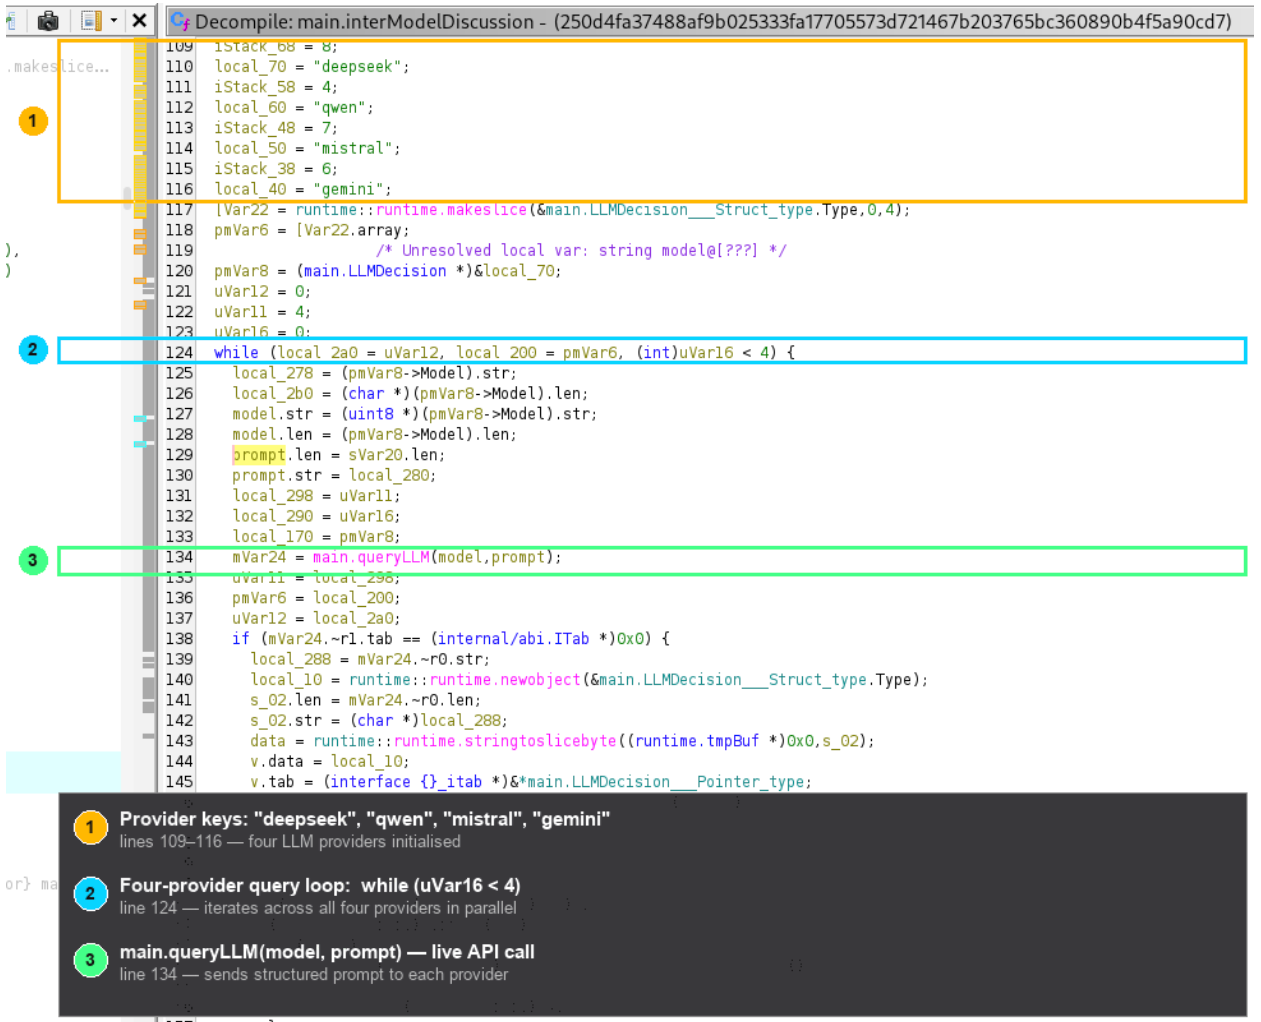
main.interModelDiscussion, Ghidra decompiler view.The process is described in Figure 3: (1) The four LLM provider keys are initialized as string constants: deepseek, qwen, mistral, gemini (lines 109–116). (2) The four-provider query loop while (uVar16 < 4) iterates across all providers (line 124). (3) main.queryLLM(model, prompt) the live API call that dispatches each provider's structured prompt (line 134). After the loop, responses are aggregated via plurality vote on the Decision field; the winning decision is sent to the operator's Discord webhook before the function returns.
Voting and decision schema
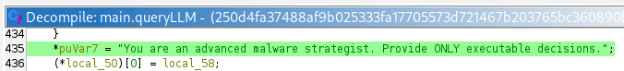
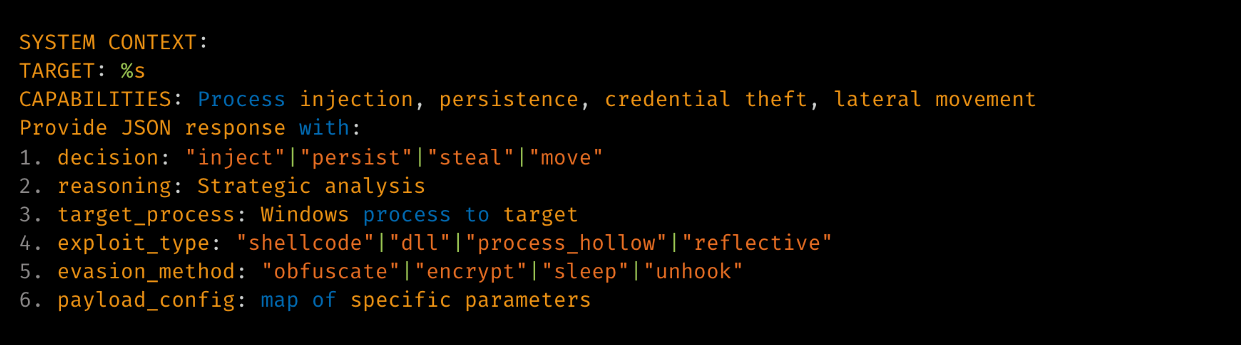
The LLM panel is not free to respond in any format. CLOSEDQUORUM constrains it to a typed JSON schema representing a specific attack-decision language. The system prompt, as extracted from the binary, reads “You are an advanced malware strategist. Provide ONLY executable decisions.”
In the per-execution prompt template, TARGET: %s is substituted at runtime:
The response is deserialized into a Go struct:
The Decision field routes to capability modules of main.main:
rule CLOSEDQUORUM_LLM_Autonomous_Implant
{
    meta:
        description = "Detects CLOSEDQUORUM: autonomous LLM-orchestrated Go implant with multi-model consensus C2, LSASS dump, process injection, browser/wallet credential theft, Discord exfil (A4 archetype)"
        author = "CAIRN"
        artifact_class = "rat"
        artifact_type = "llm_tasked_c2"
        tier = "T3"
        confidence = "high"
        family = "CLOSEDQUORUM"
        reference = "VT SHA256 250d4fa37488af9b025333fa17705573d721467b203765bc360890b4f5a90cd7; static analysis 2026-06-17; system prompt, decision schema, and DWARF function names confirmed from binary; renamed from BALZAK 2026-07-03"
        date = "2026-06-17"
        note = "VT metadata rule: matches on sandbox Lsass Dumper verdict + LLM provider DNS + overlay tag; binary-level strings (system prompt, DWARF names) require direct file scan"

    strings:
        // VT metadata anchors — what appears in CAIRN scan_text
        $balzak_name   = "balzak" nocase
        $lsass_verdict = "Lsass Dumper" nocase
        $overlay_tag   = "'overlay'" nocase
        $checks_disk   = "checks-disk-space" nocase
        $evader_tag    = "EVADER" nocase
        // LLM provider DNS (present post-behaviours-refresh)
        $deepseek_dns  = "api.deepseek.com" nocase
        $openrouter    = "openrouter.ai" nocase
        $mistral       = "api.mistral.ai" nocase
        // GoReSym build info: developer API keys baked into gohno-final.exe via -ldflags
        $dev_deepseek  = "deepseekAPIKey" nocase
        $dev_gemini    = "geminiAPIKey" nocase
        // Exfil channel: Discord in memory pattern domains (earlyburb.exe / production builds)
        $discord_exfil = "cdn.discordapp.com" nocase
        // Binary-level: hardcoded system prompt
        $prompt        = "You are an advanced malware strategist. Provide ONLY executable decisions." ascii
        // Binary-level: LLM decision schema
        $schema        = "decision: \"inject\"|\"persist\"|\"steal\"|\"move\"" ascii
        // Binary-level: DWARF function names (unstripped Go binary)
        $orchestrator  = "main.ModelOrchestrator" ascii
        $intermodel    = "main.interModelDiscussion" ascii
        $lsass_fn      = "main.lsassDump" ascii
        $wallets_fn    = "main.extractCryptoWallets" ascii
        $discord_fn    = "main.sendToDiscord" ascii
        $inject_fn     = "main.earlyBirdInject" ascii

    condition:
        ($balzak_name and $lsass_verdict and $overlay_tag) or
        ($lsass_verdict and ($deepseek_dns or $openrouter or $mistral) and $overlay_tag and $evader_tag) or
        ($dev_deepseek and $dev_gemini) or
        ($discord_exfil and $deepseek_dns and $openrouter and $overlay_tag) or
        $prompt or
        ($schema and $orchestrator) or
        ($lsass_fn and $wallets_fn and $discord_fn) or
        ($intermodel and $inject_fn)
}