
TTY Logs and the Data it Captures, (Sun, Oct 4th)

CN
CyberNew Threat Research Desk
• Original Reporting: Isc
CyberNew Threat Intel Assessment
Assessed Severity: INFORMATIONAL
Impacted Surface
Enterprise Perimeter & Network Defense
Intelligence Sector
Defensive Security & Blue Team

Analyst Takeaway

"For an experiment, I created a script [ 1 ] that parses and send the TTY logs collected from actors or bots activity that run various commands after they successfully login the DShield sensor. Those TTY logs are sent daily at the end of each day to the DShield SIEM [ 2 ] to be correlated with all the data. The following ES|QL query provides a summary of all contab commands matching a TTYLog hash..."

Recommended Defense & Mitigation

  • Threat Monitoring: Ingest published IOCs into SIEM/EDR detection rules for continuous telemetry monitoring.
  • Security Awareness: Alert staff and maintain baseline endpoint hardening across endpoints.
Curated & Verified by CyberNew Threat Intelligence Desk Standard Defense Framework (NIST / MITRE ATT&CK)

For an experiment, I created a script [1] that parses and send the TTY logs collected from actors or bots activity that run various commands after they successfully login the DShield sensor. Those TTY logs are sent daily at the end of each day to the DShield SIEM [2] to be correlated with all the data. 

The following ES|QL query provides a summary of all contab commands matching a TTYLog hash performed by different actors while logged in the sensor over a 90 day period. 

TTYLogs Correlation

FROM cowrie* 
| WHERE transaction.id == "f904275333aeac48d7df6cf53fe5fb9212c7d132a7d37253d2ab9321ba2690d8"
| WHERE event.hash IS NOT NULL
| KEEP transaction.id, event.hash
| STATS Total=COUNT(event.hash) BY event.hash, transaction.id
| SORT Total DESC


This transaction ID captured 5 similar crontab commands that are translated from its hash equivalent into this list executed by more than 3130 different actors (IPs):
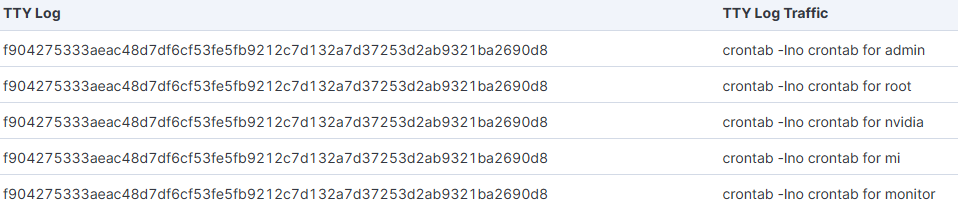
TTYLogs Sources

transaction.id: f904275333aeac48d7df6cf53fe5fb9212c7d132a7d37253d2ab9321ba2690d8 over a 90 day period

Source Verification & Original Intelligence

This threat report was reviewed by CyberNew analysts and cross-referenced with primary security disclosures from Isc.

Primary Advisory →