
Vulnerabilities & CVEs BleepingComputer 1 month ago

US warns of AI-powered attacks on Siemens PLCs in critical infrastructure

CN
CyberNew Threat Research Desk
• Original Reporting: BleepingComputer
CyberNew Threat Intel Assessment
Assessed Severity: CRITICAL
Impacted Surface
Enterprise Perimeter & Network Defense
Intelligence Sector
Vulnerabilities & CVEs

Analyst Takeaway

"U.S. cybersecurity agencies warn that threat actors are using AI-generated scripts to exploit Siemens S7 Series programmable logic controllers (PLCs) in U.S. critical infrastructure. PLCs are industrial computers used to automate and control machinery and physical processes in factories and other critical infrastructure. The NSA, CISA, FBI, Department of Energy, and Environmental Protection..."

Recommended Defense & Mitigation

  • Emergency Patching: Prioritize vendor patches and CVE mitigation across internet-facing assets immediately.
  • Perimeter Audit: Inspect perimeter firewall logs and hunt for unauthorized RCE indicators.
Curated & Verified by CyberNew Threat Intelligence Desk Standard Defense Framework (NIST / MITRE ATT&CK)

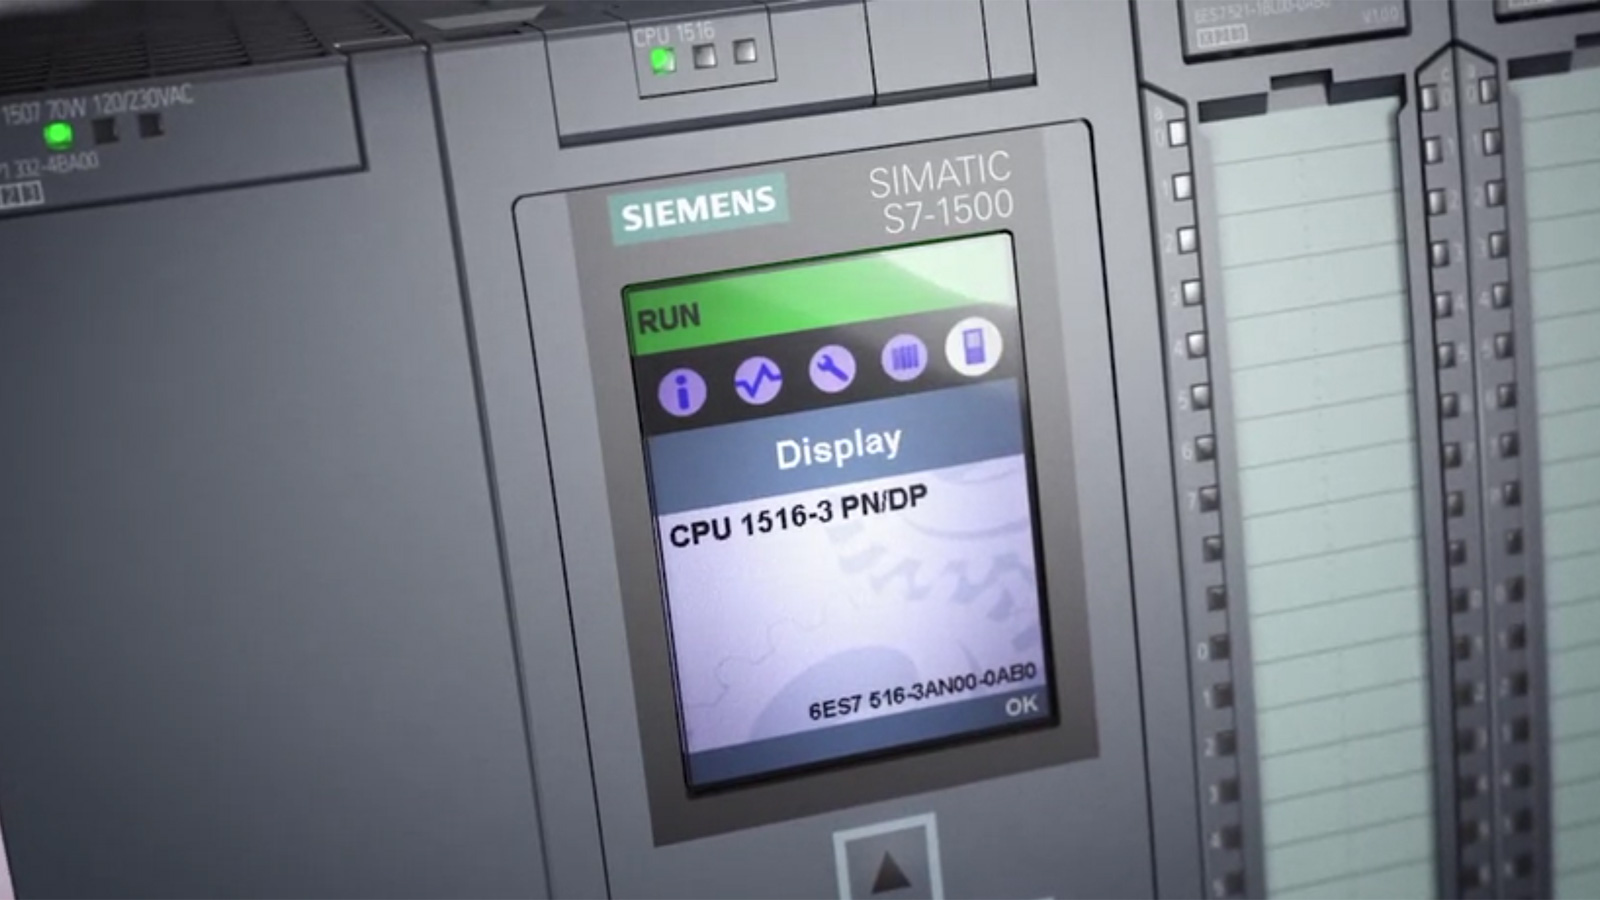
Siemens S7-1500

U.S. cybersecurity agencies warn that threat actors are using AI-generated scripts to exploit Siemens S7 Series programmable logic controllers (PLCs) in U.S. critical infrastructure.

PLCs are industrial computers used to automate and control machinery and physical processes in factories and other critical infrastructure.

The NSA, CISA, FBI, Department of Energy, and Environmental Protection Agency issued the joint advisory Wednesday, saying the attacks are ongoing.

Get the report

Source Verification & Original Intelligence

This threat report was reviewed by CyberNew analysts and cross-referenced with primary security disclosures from BleepingComputer.

Primary Advisory →